Enterprise AI Agent Production Security and Evaluation Checklist
Agents select tools and execute multi-step work. Production risk therefore goes beyond an incorrect answer: the agent may call the wrong tool, hold excessive permissions, expose sensitive data or continue operating in an abnormal state. A structured checklist should validate both business and technical boundaries.
Define Business Success, Not Only Model Quality
Specify the business metric the agent should improve, such as handling time, manual steps, first resolution, retrieval accuracy or report completion. Output that merely looks impressive is not an acceptance standard.
Create a Permission Matrix for Every Tool
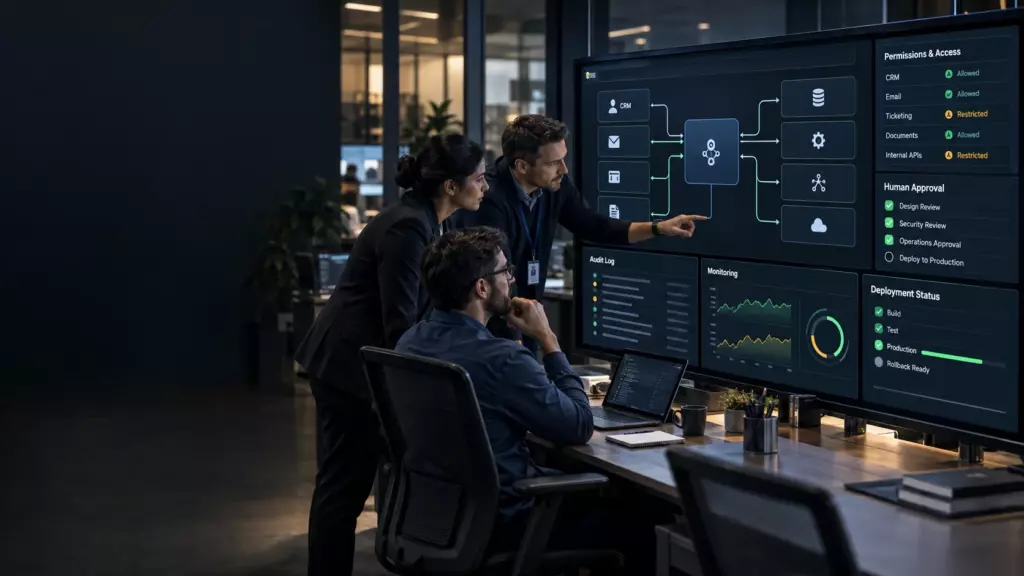
List what the agent may read, create, modify and delete. Start with read-only access, test environments and dedicated identities. Restrict scope by customer, project or data range, and require separate approval for high-risk access.
Place Human Approval at Clear Boundaries
External communication, production writes, deletion, payment, contractual commitments and sensitive access should require confirmation. The reviewer should see the proposed action, target and evidence, not only a generic continue button.
Validate Data and Context Boundaries
Review whether knowledge, conversation history, uploads, system responses and tool output can mix data that should remain separate. Enforce isolation across users, departments, clients and projects.
Test Attacks, Exceptions and Invalid Input
Test prompt injection, malicious documents, oversized input, missing fields, conflicting instructions, tool timeouts, API errors and duplicate requests. The system should refuse, stop, retry or escalate rather than continuing indefinitely.
Prepare Failure Handling and Human Takeover
Define timeouts, retry limits, idempotency, duplicate-write protection, undo and compensation. A human taking over should receive the complete context and actions already performed.
Maintain Traceable Logs
Record requests, retrieval sources, model decisions, tool parameters, tool results, approvals and final output while avoiding unnecessary long-term storage of sensitive data.
Use a Representative Evaluation Set
Include normal, boundary, failure and high-risk cases with expected outcomes. Re-run the set after model, prompt, knowledge or tool changes so regressions do not go unnoticed.
Monitor Cost and Business Outcomes
Track success, human intervention, latency, token and tool cost, failure causes and business feedback. An agent is an operated system, not a one-time automation script.
Lanever’s enterprise agent integration and governance service covers systems, least privilege, approvals, logs, monitoring and rollback. An AI assessment and FDE engagement can define the pilot boundary first.